


The parent company of fashion brands favoured by the Princess of Wales has apologised to customers after it was hit by a cyber attack.
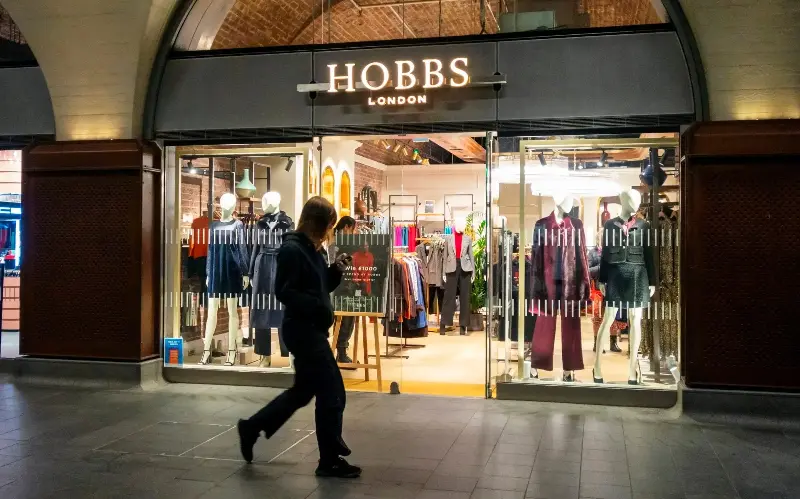
The Foschini Group (TFG) London – the fashion group that includes Hobbs and Whistles, whose dresses and coats have often been worn by the Princess – told customers on Tuesday that it had suffered a “cyber security incident”.
The South African retail group said it became aware of the attack affecting its UK business on Sunday.
It said the hack had affected “certain of its IT systems” – specifically its Phase Eight, Hobbs and Whistles brands.
The company said there was no reason to believe customers’ payment information was at risk.
In an email to customers, the company said: “On Sunday 11th October, TFG London identified a cyber security incident affecting some of our IT systems.
“As soon as we identified the incident, we activated our business continuity plan, engaged external cyber security experts and informed relevant authorities. Our investigation is ongoing and we are working hard to get all our systems back up and running as quickly and safely as we can.
“All our stores are open as normal and our teams will be happy to welcome you.”
Orders made on or after Sunday may be delayed, the company warned, but it urged customers not to reorder.
TFG is the latest retailer to suffer a cyber attack, after Asos confirmed a potential data breach after hackers sent a smartphone alert to thousands of its customers.
Asos said last week that the hackers tricked an employee into sharing login details. The hackers gained access to some personal information, including names and contact details. However, it is thought that no payment card information or account passwords were accessed.
TFG first entered the UK market in 2015 by buying Phase Eight and has since added womenswear brands Whistles and Hobbs, homeware brand Inside Story and lifestyle brand White Stuff to its portfolio.
Headquartered in London, the group now employs 3,000 people. Inside Story and White Stuff have not been affected by the cyber attack.
In an email to customers, TFG said it did not believe any payment information had been stolen.
“Importantly, payment processing is carried out by a third-party provider,” the email said. “Based on our investigation so far, we have no reason to believe that payment information is at risk.
“As our investigation continues, we will be working to identify if any sensitive information related to our customers was impacted.
“If we determine that your personal information was affected, you will be directly informed. We do not believe it is necessary to change your account login information at this time.
“We know this news may be unsettling and we’re committed to keeping you updated as we have more information to share.”